

Cybersecurity Consulting
What does a cybersecurity audit entail?
Request more information about your cybersecurity scan here. This scan is available for up to 300 employees; a larger scan can be conducted upon request.
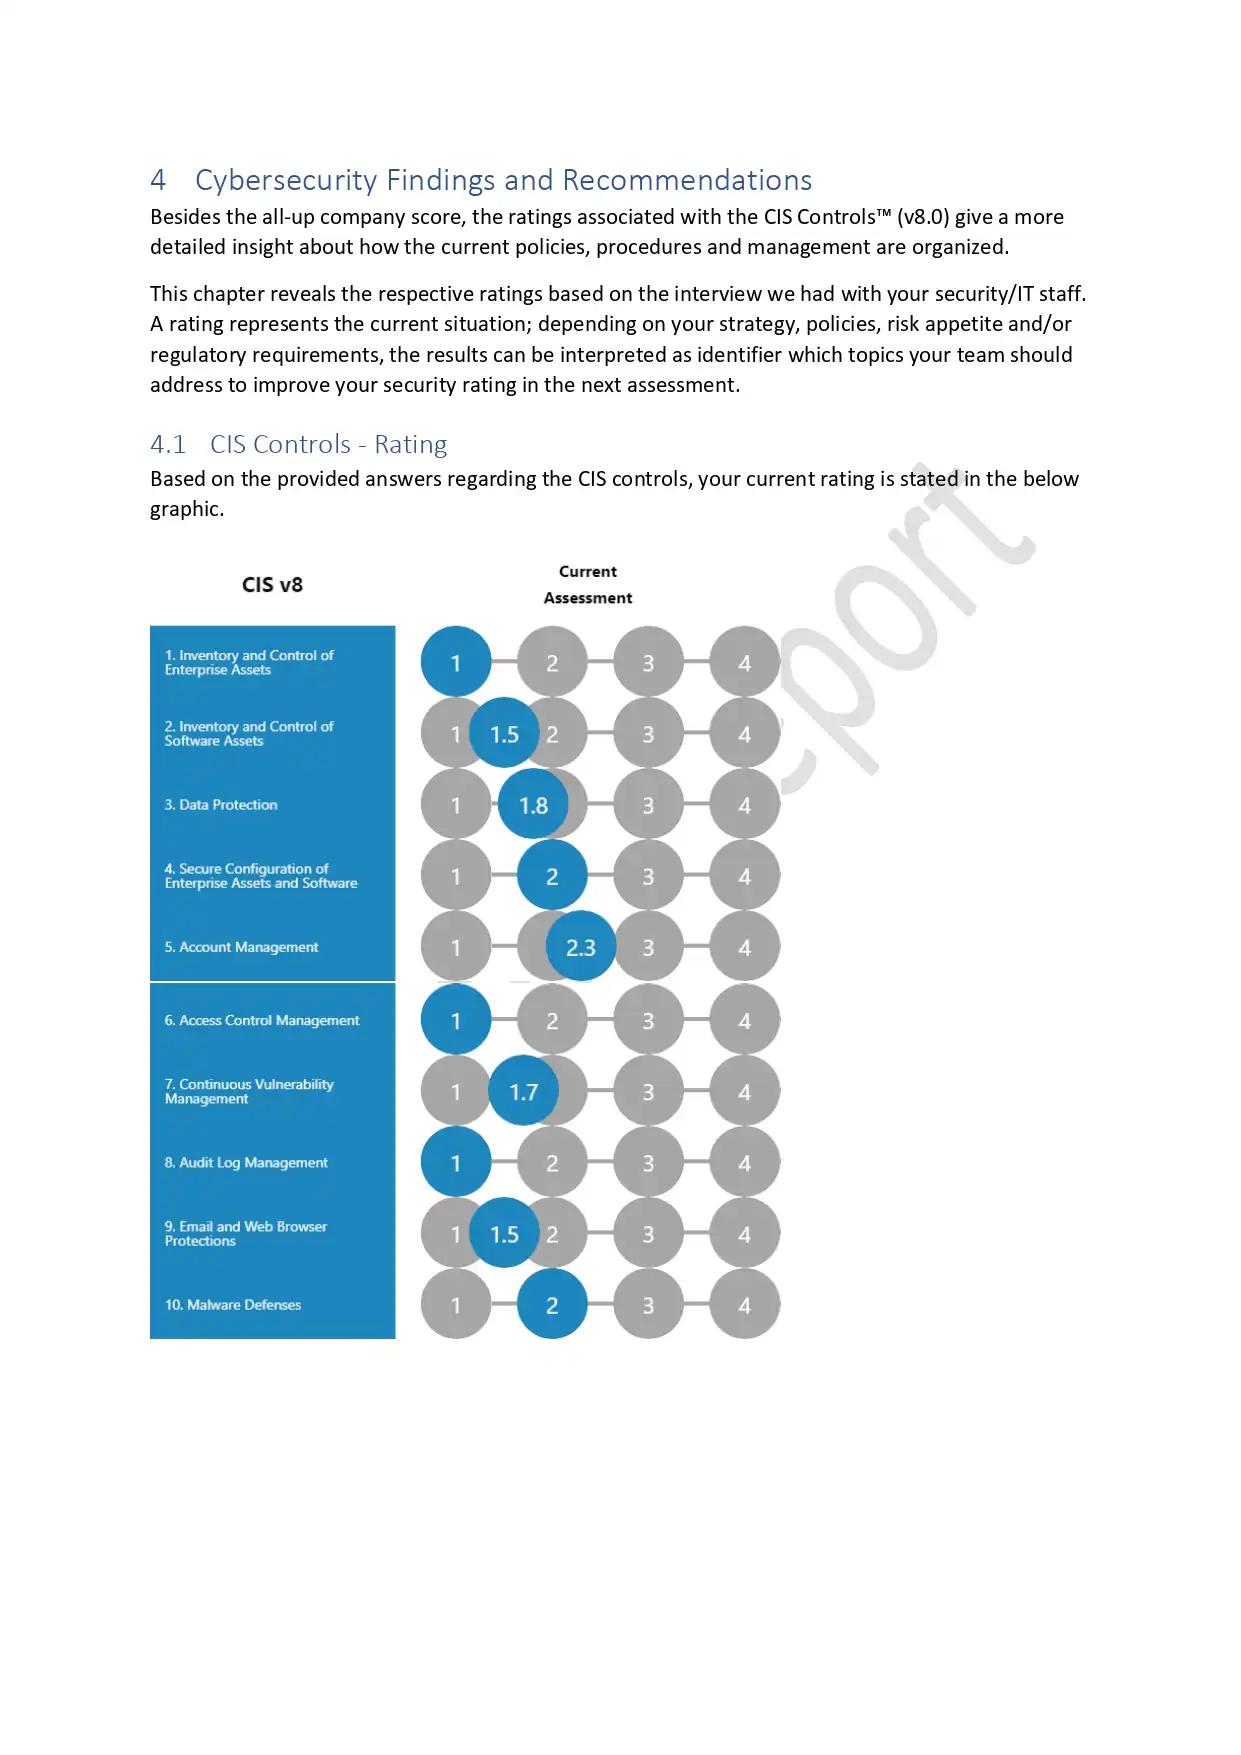
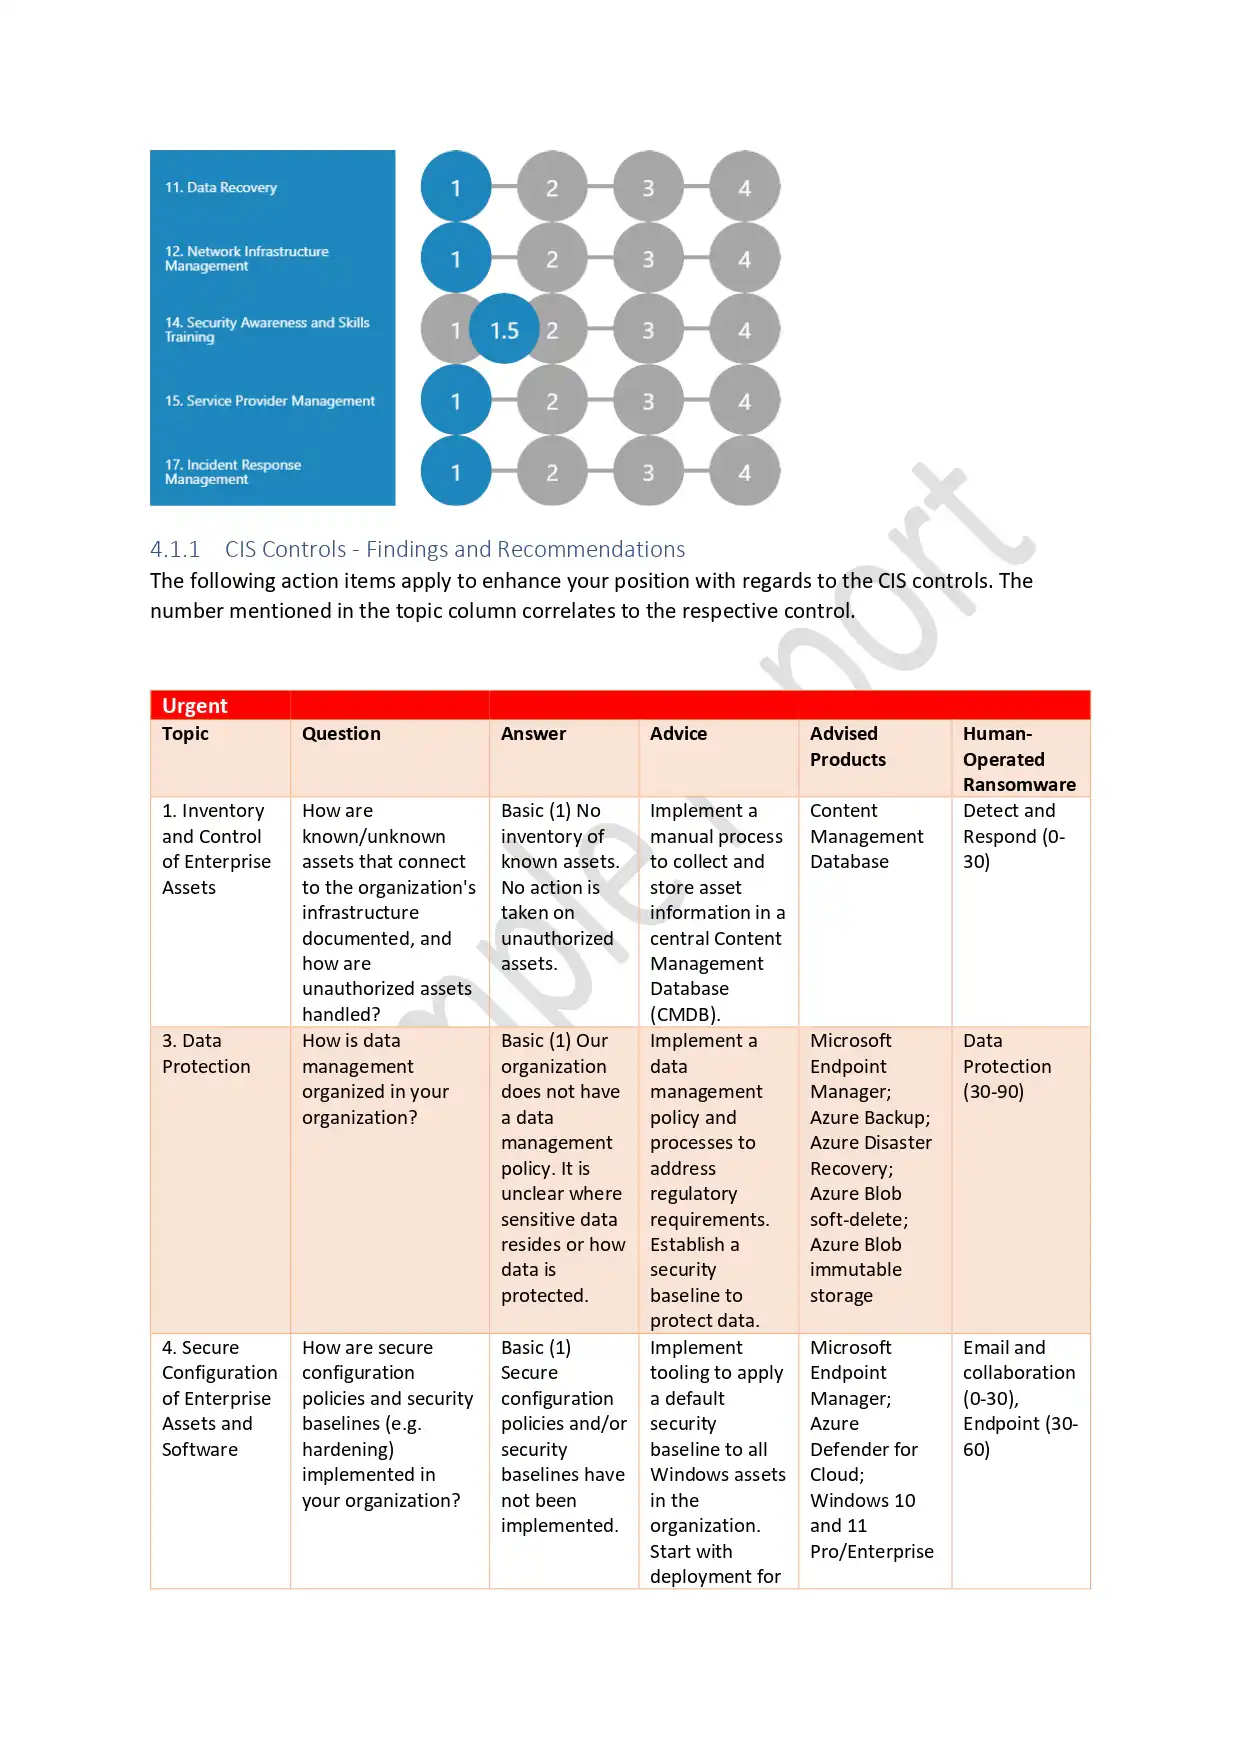
To assess your cybersecurity, you'll receive a security score for each CIS control in the following areas:
- Inventory and Control of Enterprise Assets
- Inventory and Control of Software Assets
- Data Protection
- Secure Configuration of Enterprise Assets and Software
- Access Control Management
- Continuous Vulnerability Management
- Audit Log Management
- Email and Web Browser Protections
- Malware Defense
- Data Recovery
- Network Infrastructure Management
- Security Awareness and Skills Training
- Incident Response Management
What does the cybersecurity scan entail?
The cybersecurity audit is conducted via the CSAT tool and is based on the best practices framework of Center for Internet Security.
CIS is a nonprofit organization with globally recognized best practices for securing IT systems and data. They are also responsible for the CIS Controls® and CIS Benchmarks™.
Price
How much does a cybersecurity audit cost?
A cybersecurity assessment is much less expensive than the costs associated with a breach! That’s why you should choose our One-time Security Six Scan for €6,000 and find out where and how you can improve your cybersecurity!
Security Six Scan & NIS2 Compliance
€6.000
- Security Audit of Your Environment
- In-depth interview based on CIS Controls and CCB Cyberfundamentals
- Comprehensive Security Report
- Roadmap & Action Plan for Full NIS2 Compliance
- Explanation by a cybersecurity consultant
Sample Security Report
What does the report say?
The Cyber Security Assessment Tool comes with a clear plan of action to improve your organization's cybersecurity, exactly where it's needed.
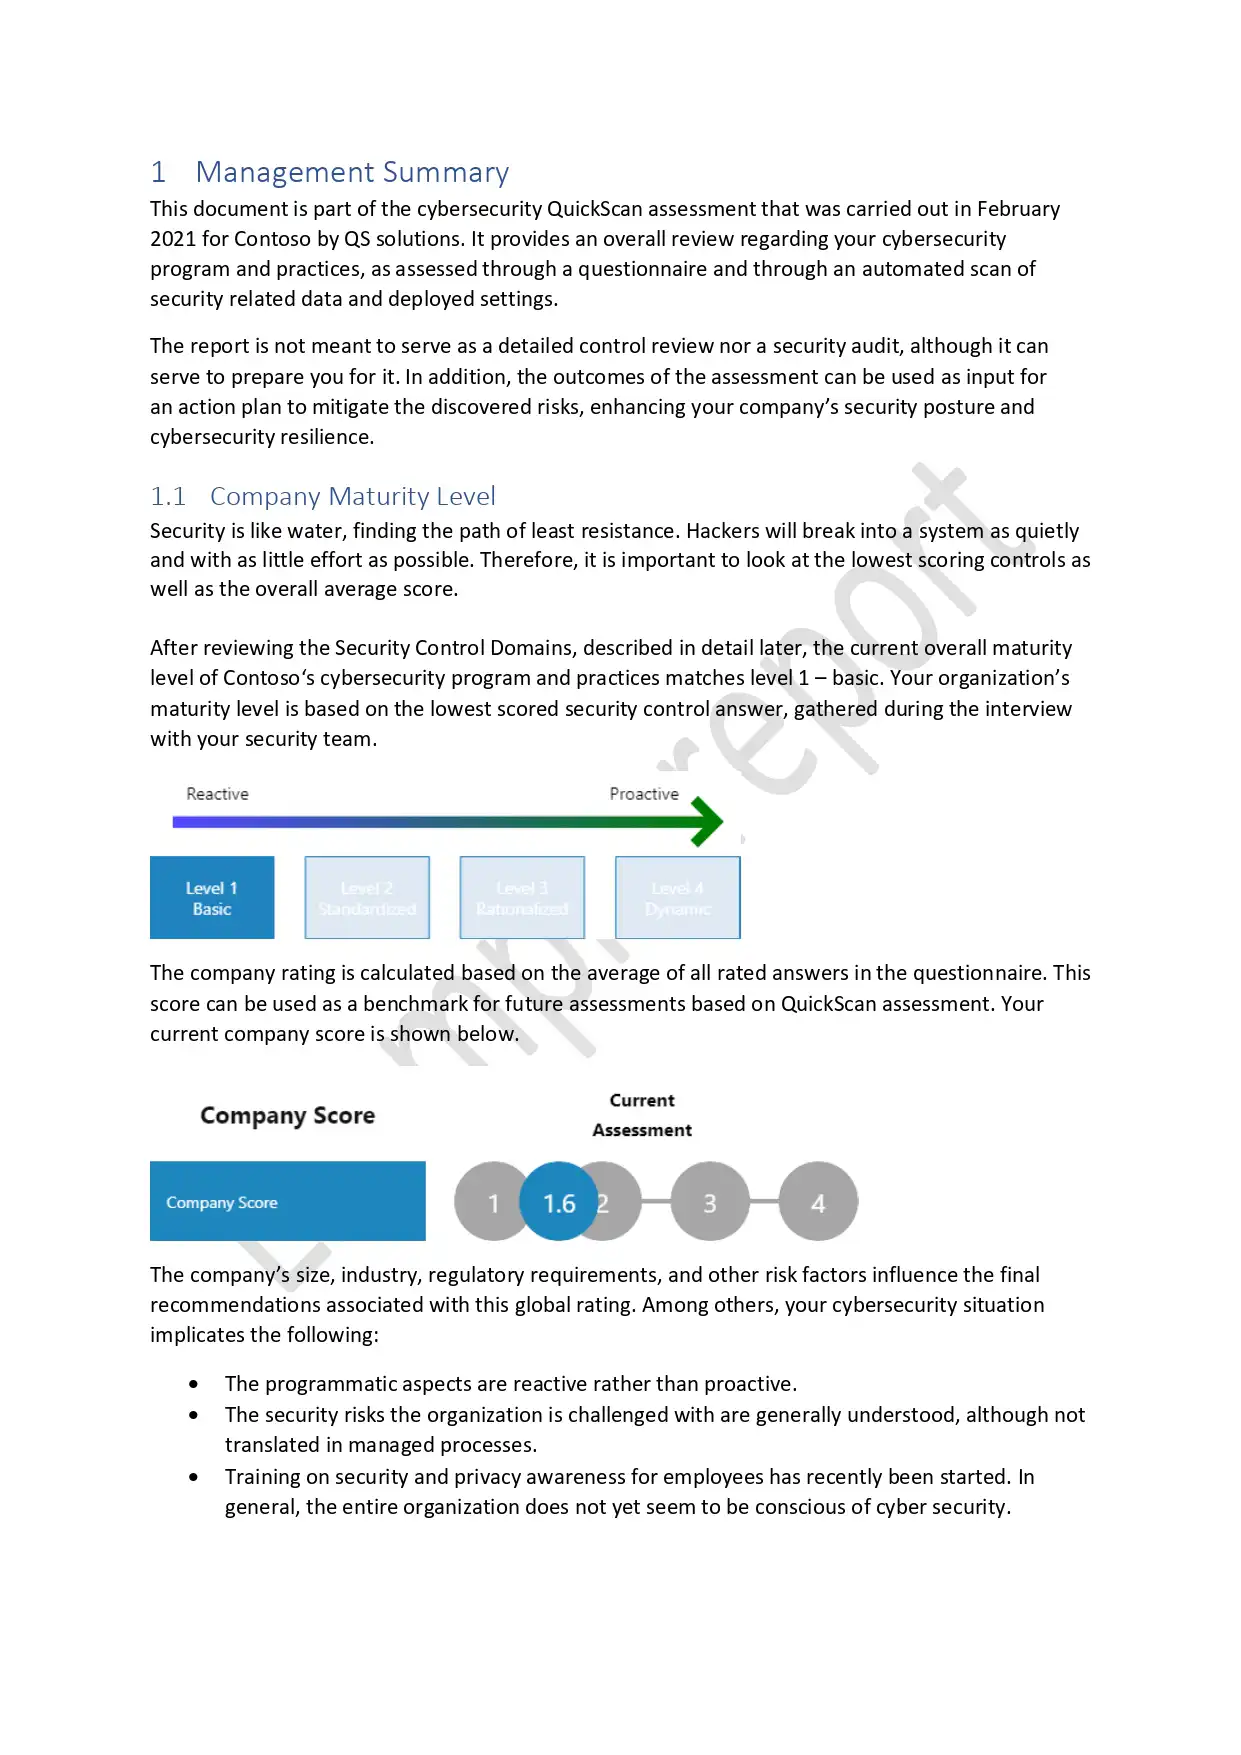
- Management Summary for Non-IT Professionals
- Company Maturity Level
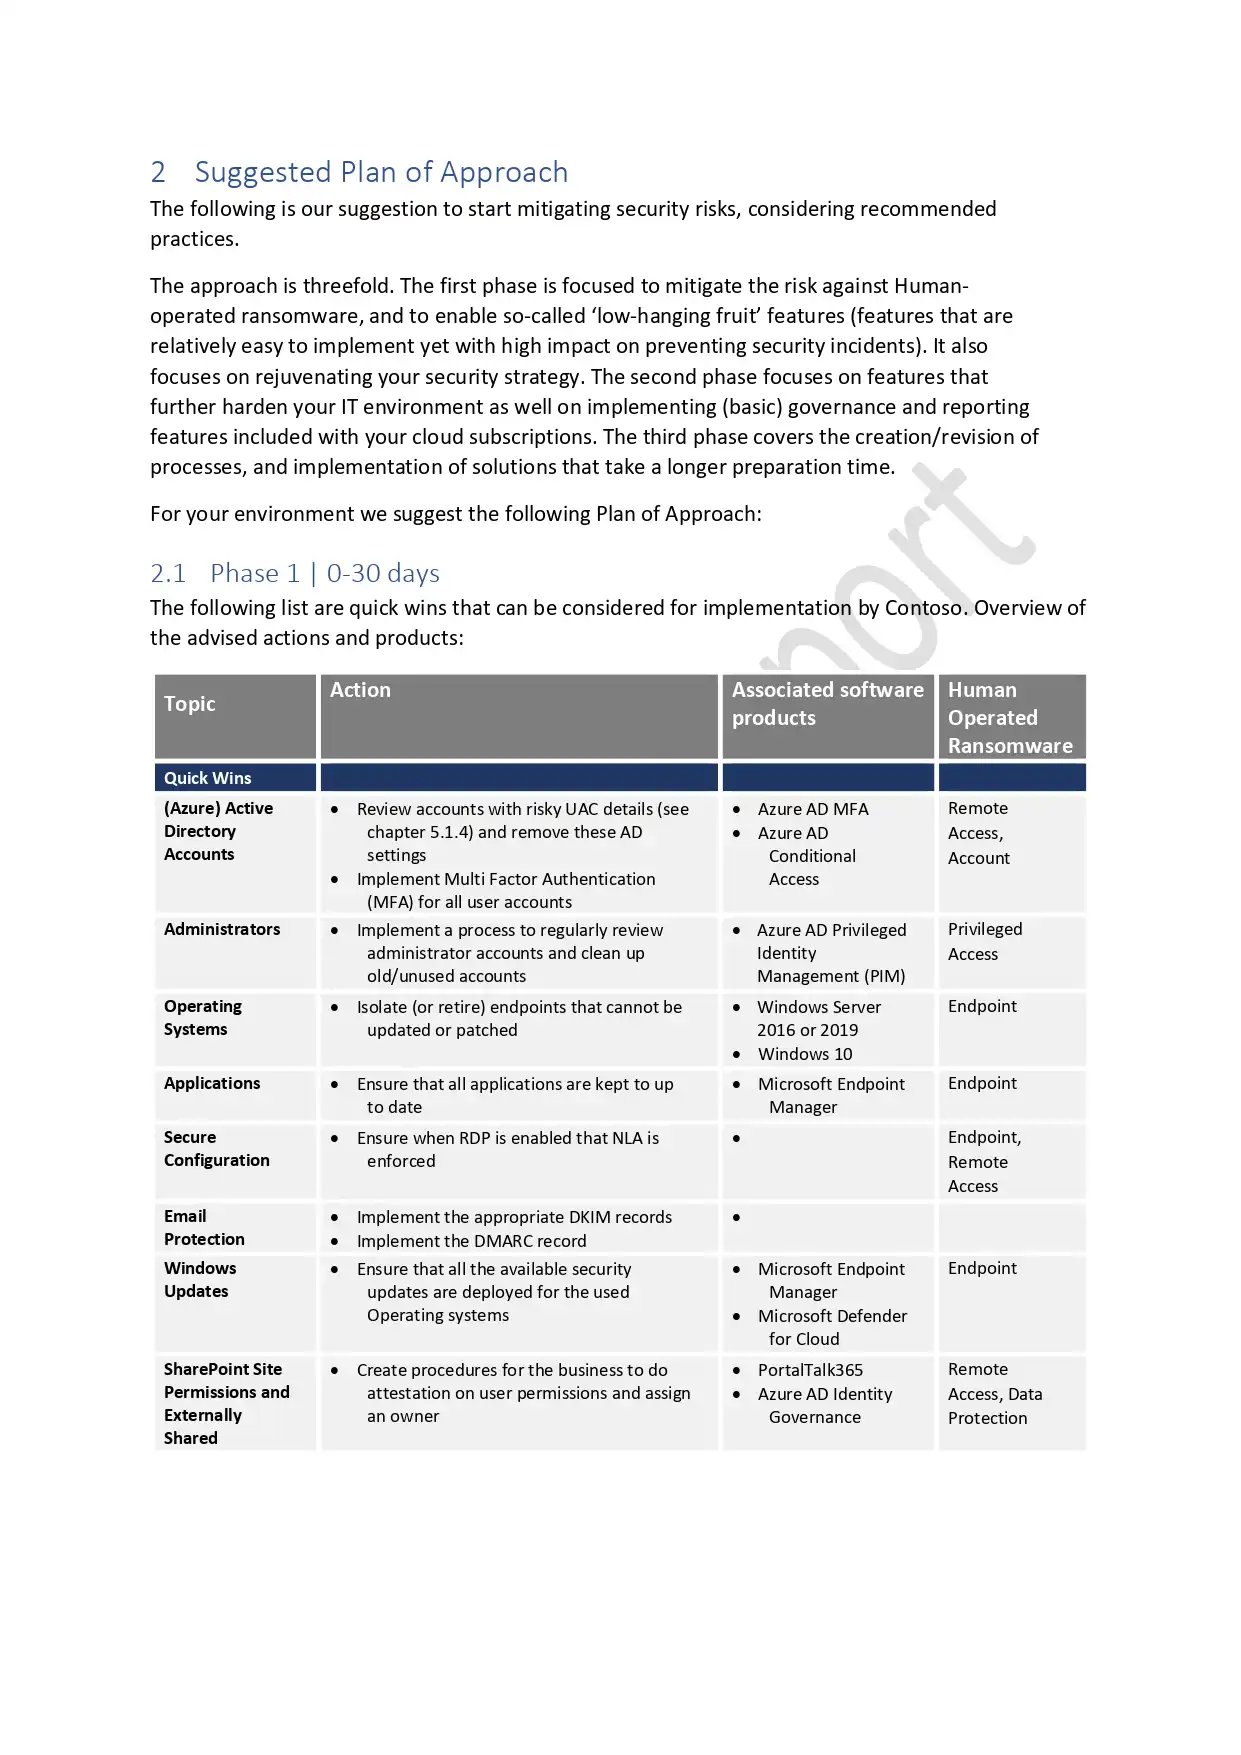
- Strategic Recommendations
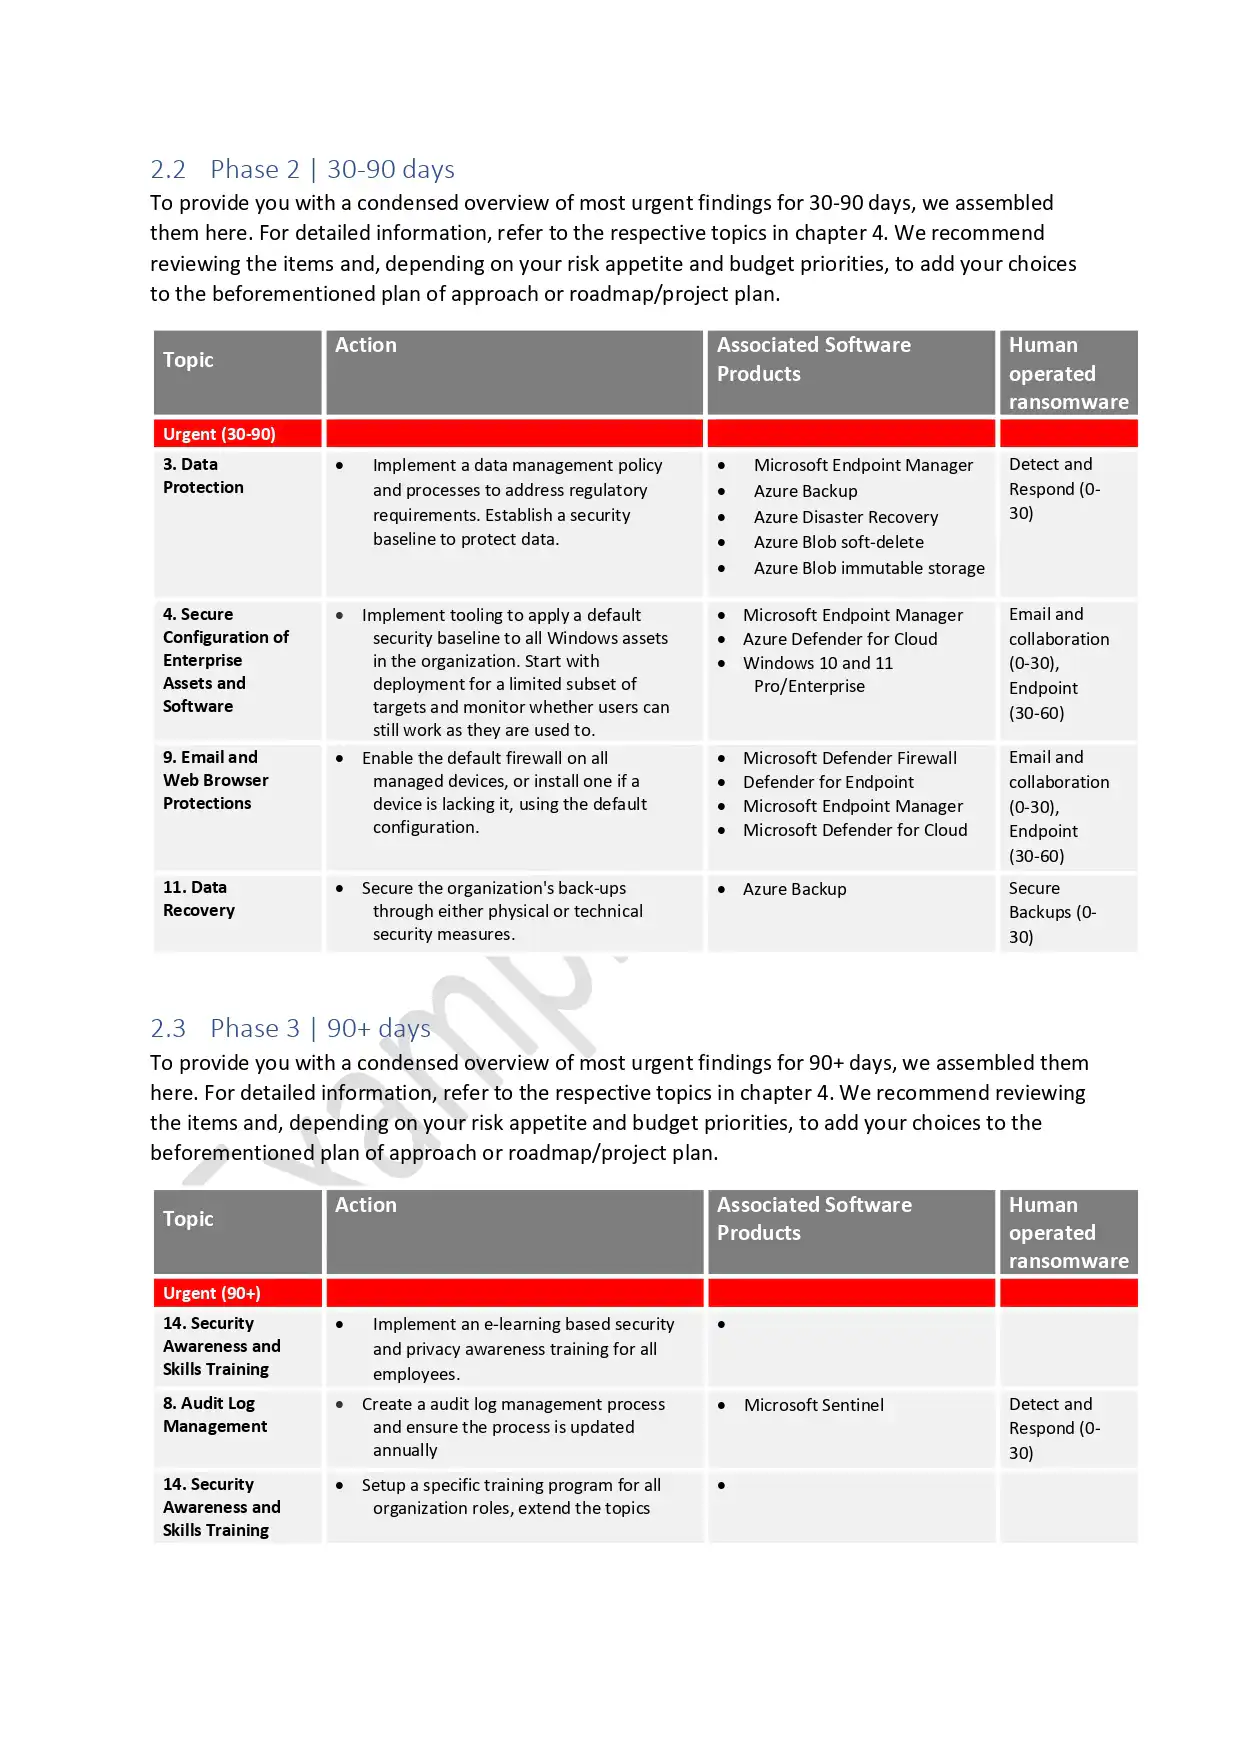
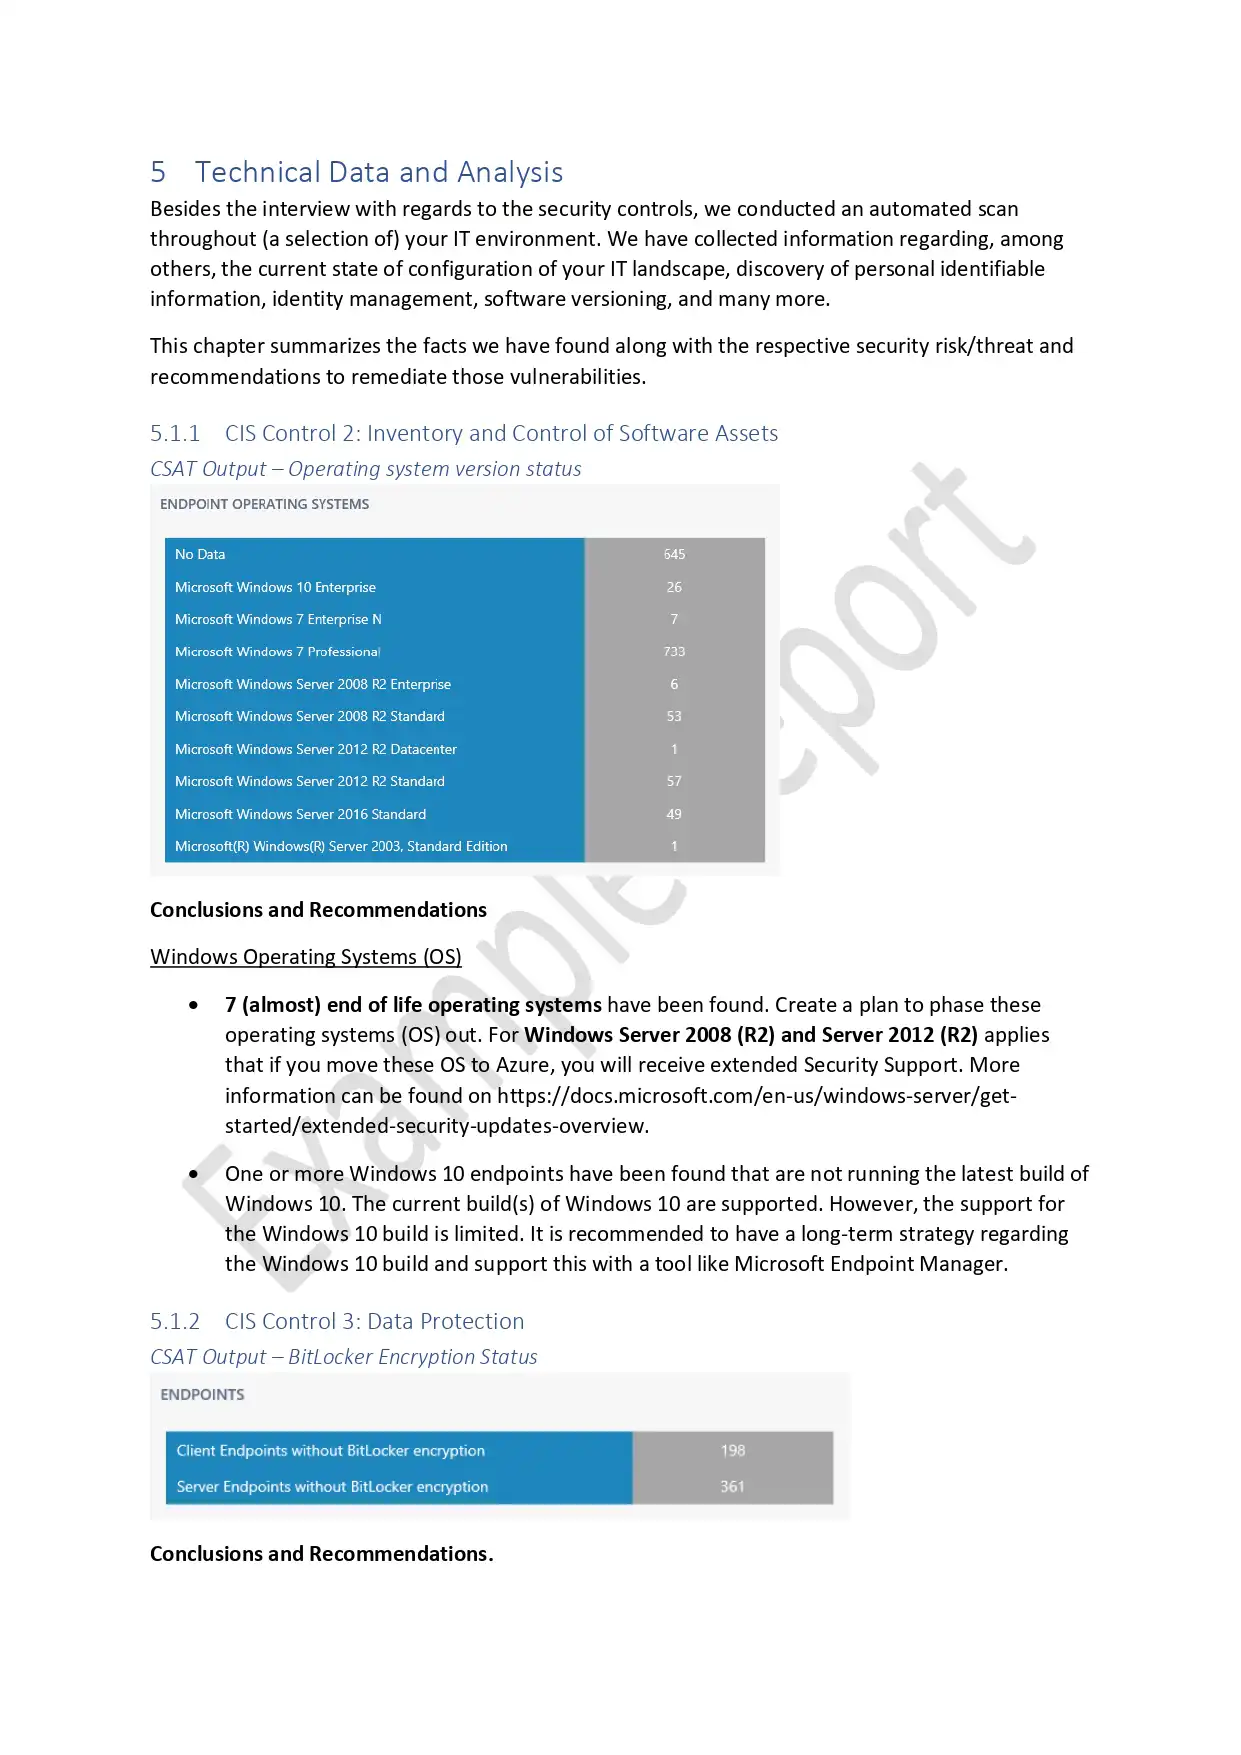
- Action Plan Based on Urgency
- CIS Inspections
- Score of 4
- Findings and Recommendations
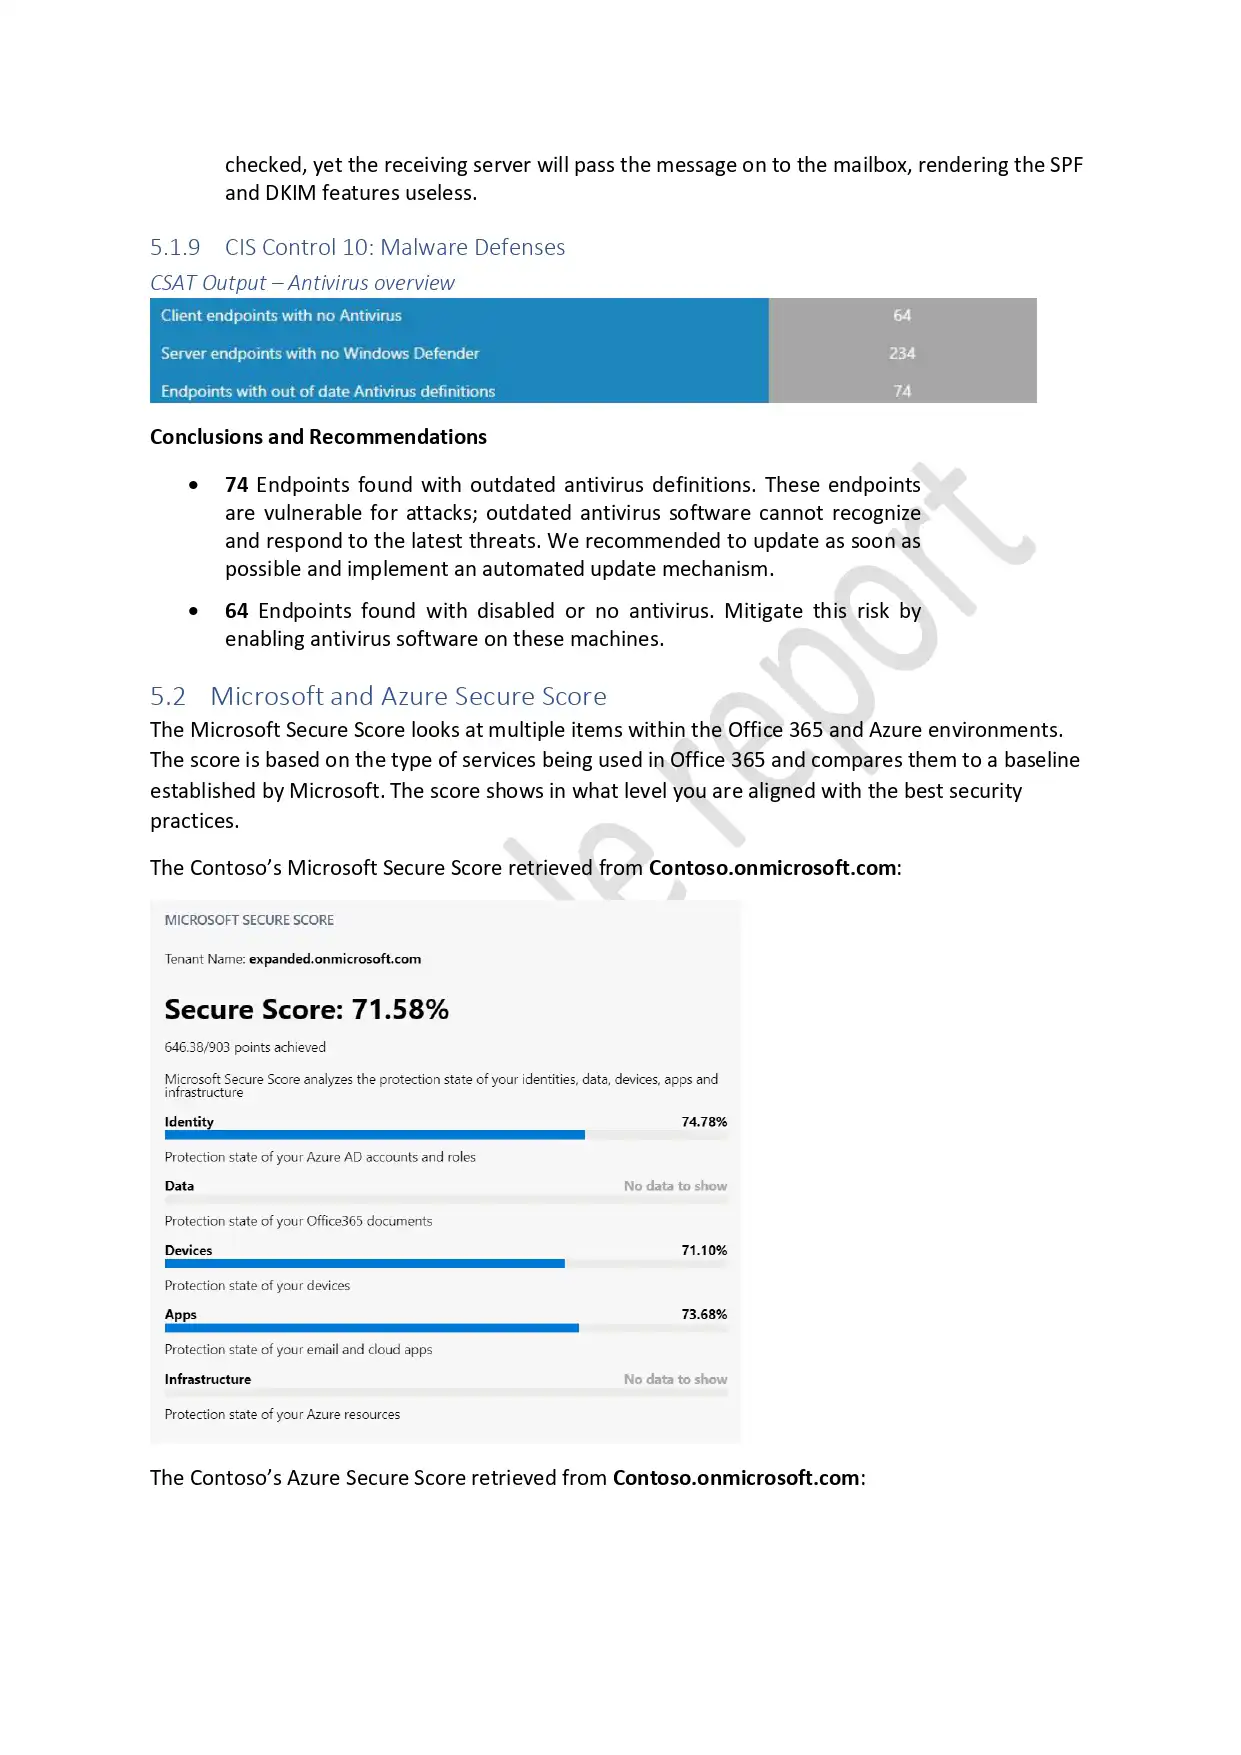
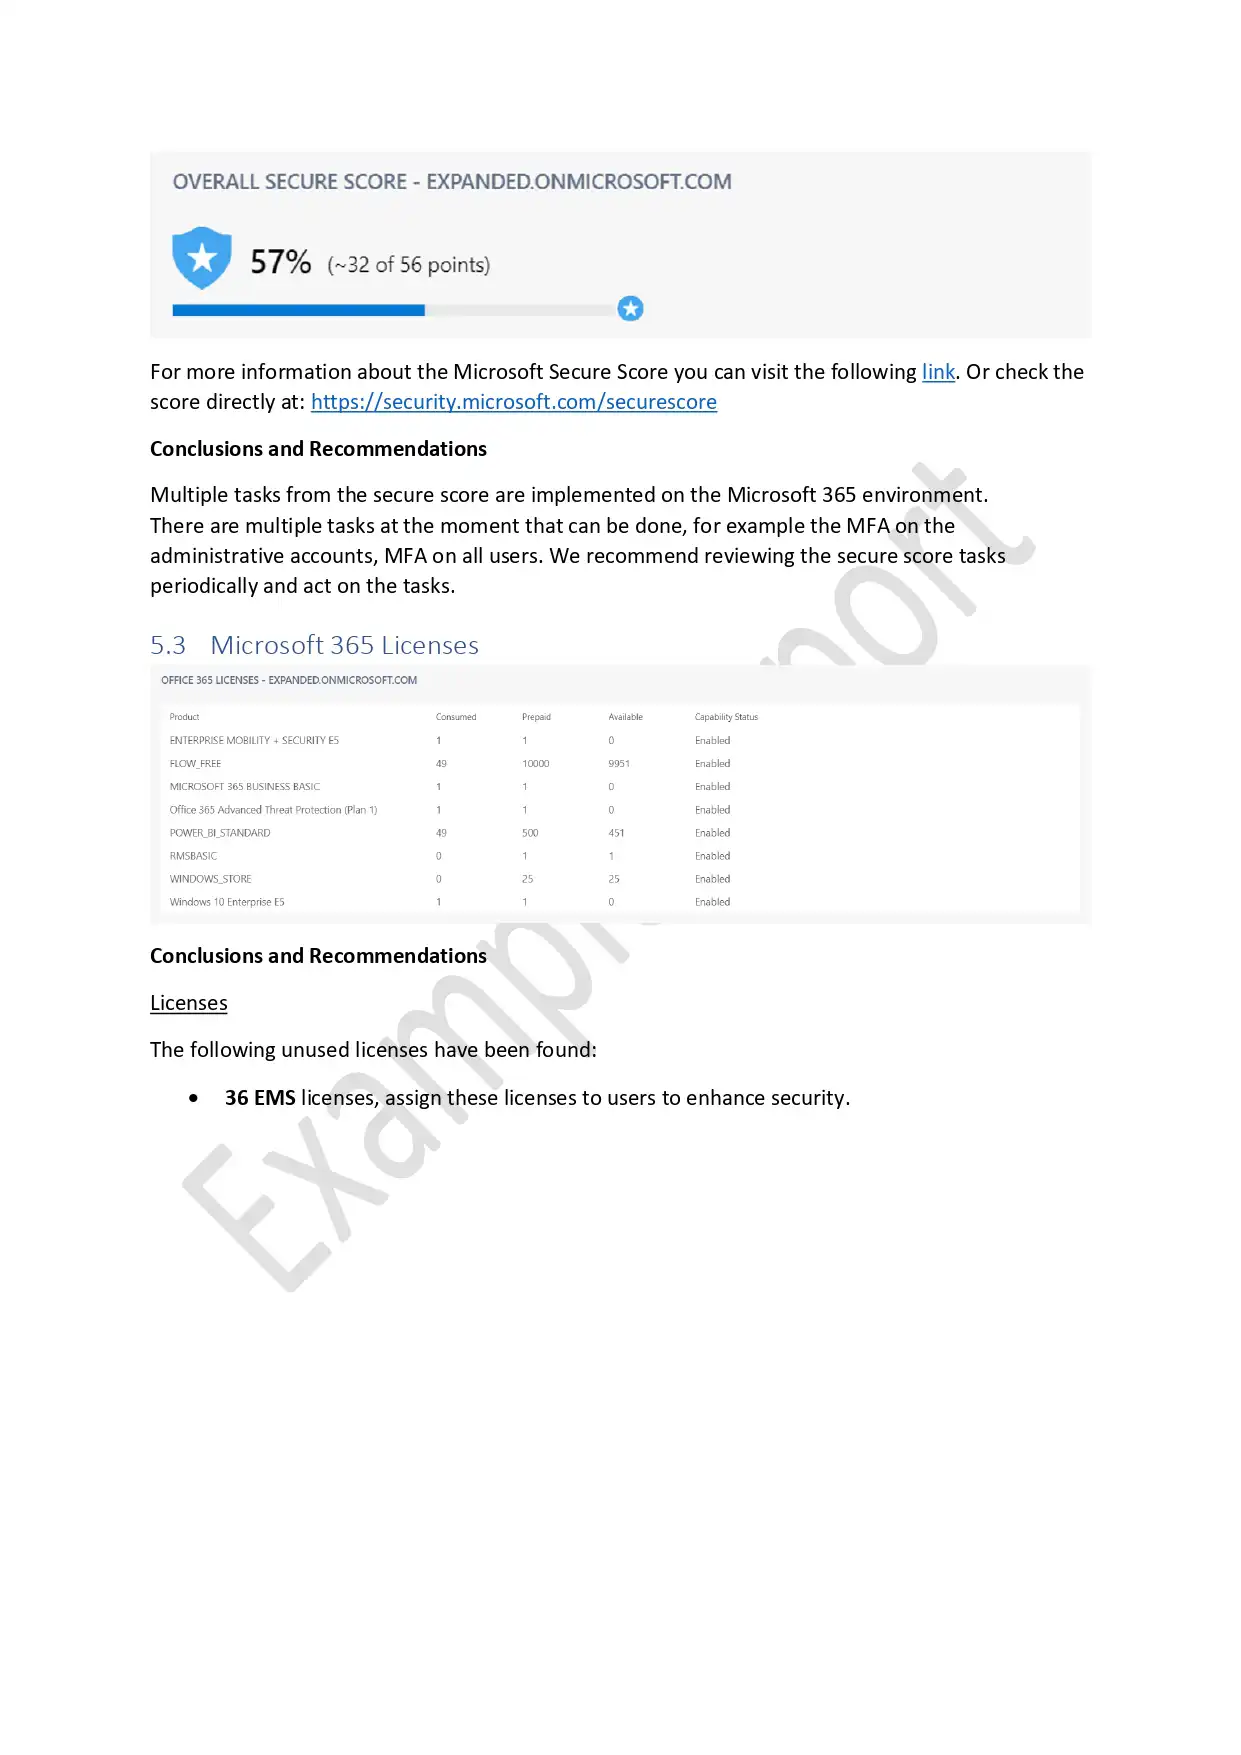
- Technical Data and Analysis
Step-by-Step Guide
The Security Six Scan Process
A comprehensive assessment of your IT infrastructure in just 3 weeks.
1
1. Intake and Installation
Interview with Alistar, a cybersecurity specialist, and installation of the CSAT tool in your IT environment (virtual/on-premises/cloud).
2
2. Scan the surroundings
We analyze the endpoints—Local Active Directory, Microsoft 365, Azure, SharePoint, etc.—and we interview the key stakeholders.
4
3. Analysis
The cybersecurity consultant analyzes this data, and the results are documented in a comprehensive final report.
3
4. Recommendations
The cybersecurity consultant will review the action plan—including the recommended measures and the scores for your environment—with you. You will receive the full report.
E-book: Security Six Strategy
Learn more about the 6 pillars of a strong cybersecurity strategy. Discover common risks and hacker techniques. You’ll also learn the best ways to protect yourself—from quick fixes to professional security advice.

Why conduct an audit?
The Importance of a Cybersecurity Audit
Discover exactly where the threats or risks lie within your organization to avoid the costs of a data breach. This way, you can keep your sensitive data protected, maintain customer trust, ensure business continuity, keep employees satisfied, and avoid the costs of a data breach by identifying weaknesses in your organization.
Business Continuity
The worst-case scenario that every manager wants to avoid is having to shut down the company for a period of time because, for example, systems have been hacked or data has been encrypted. A IT Security Strategy enhances business continuity.
Risk Mitigation
In addition to the immediate risks of a cyberattack, there are also long-term risks such as damage to your reputation, loss of customers, and data loss. Minimize these risks by focusing on the right IT Security Solutions.
Data Protection
Companies often have sensitive data—such as customer information, financial data, and proprietary information—that must be protected. Cybersecurity helps ensure that this data is not accessed or stolen by unauthorized individuals.
Employee Satisfaction
No frustrated employees lining up at the IT help desk because of difficult login screens, annoying “are you a robot?” puzzles, and confusing portals. No delays or technical VPN issues that hinder their work. The feeling that their work is valuable and not just at risk.
How healthy is your IT environment?
Give your IT environment a thorough health check—before something goes wrong. Request a free audit, and we’ll assess your organization’s current IT situation: infrastructure, software, security, backups, and work processes.

Our Modern Work team is here to help you
Alistar is a Microsoft Certified Partner and has a team of experienced business consultants, engineers, and experts who are happy to guide you through the entire process. Our goal is to make your journey as smooth as possible.

Jo Geeraerts


